CyberHeist Click Bait
By Srijan Parmar · 1 min read
About the CTF: CyberHeist
Cyber Heist Challange Click-Bait
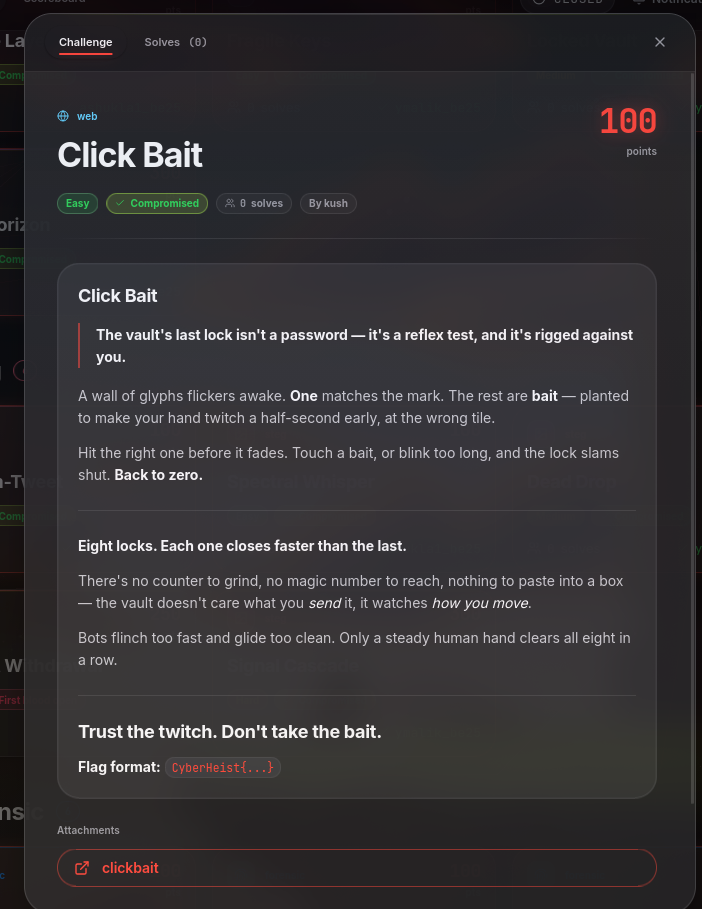
The challenge
Cyber Heist Challange Click-Bait
First look
Finding the way in
tried inspecting the website's JavaScript As Always, tried finding some valid clicks or glyphs.Found RSA key and edited the JWT for admin privelleges. After testing different key formats, we found that adding a trailing newline to the PEM key allowed the forged token to pass authentication.
# the command you ran
Ran some fetch and console logs in the end of a loop if they found some thing intersting
The flag
Using the forged token, we gained admin access and opened the restricted vault through account ID 31337.
The server returned the Flag: CyberHeist{4lgc0nfus10nc0ldst0r4g3r41d}
What I learned
WEB questions were no joke