Fragile Keys
By Srijan Parmar · 1 min read
About the CTF: CyberHeist
First, we extracted two files from the zipfile, ciphertext.txt and publickey.txt files. The public key contained the RSA modulus and public exponent (e = 65537), along with the en…
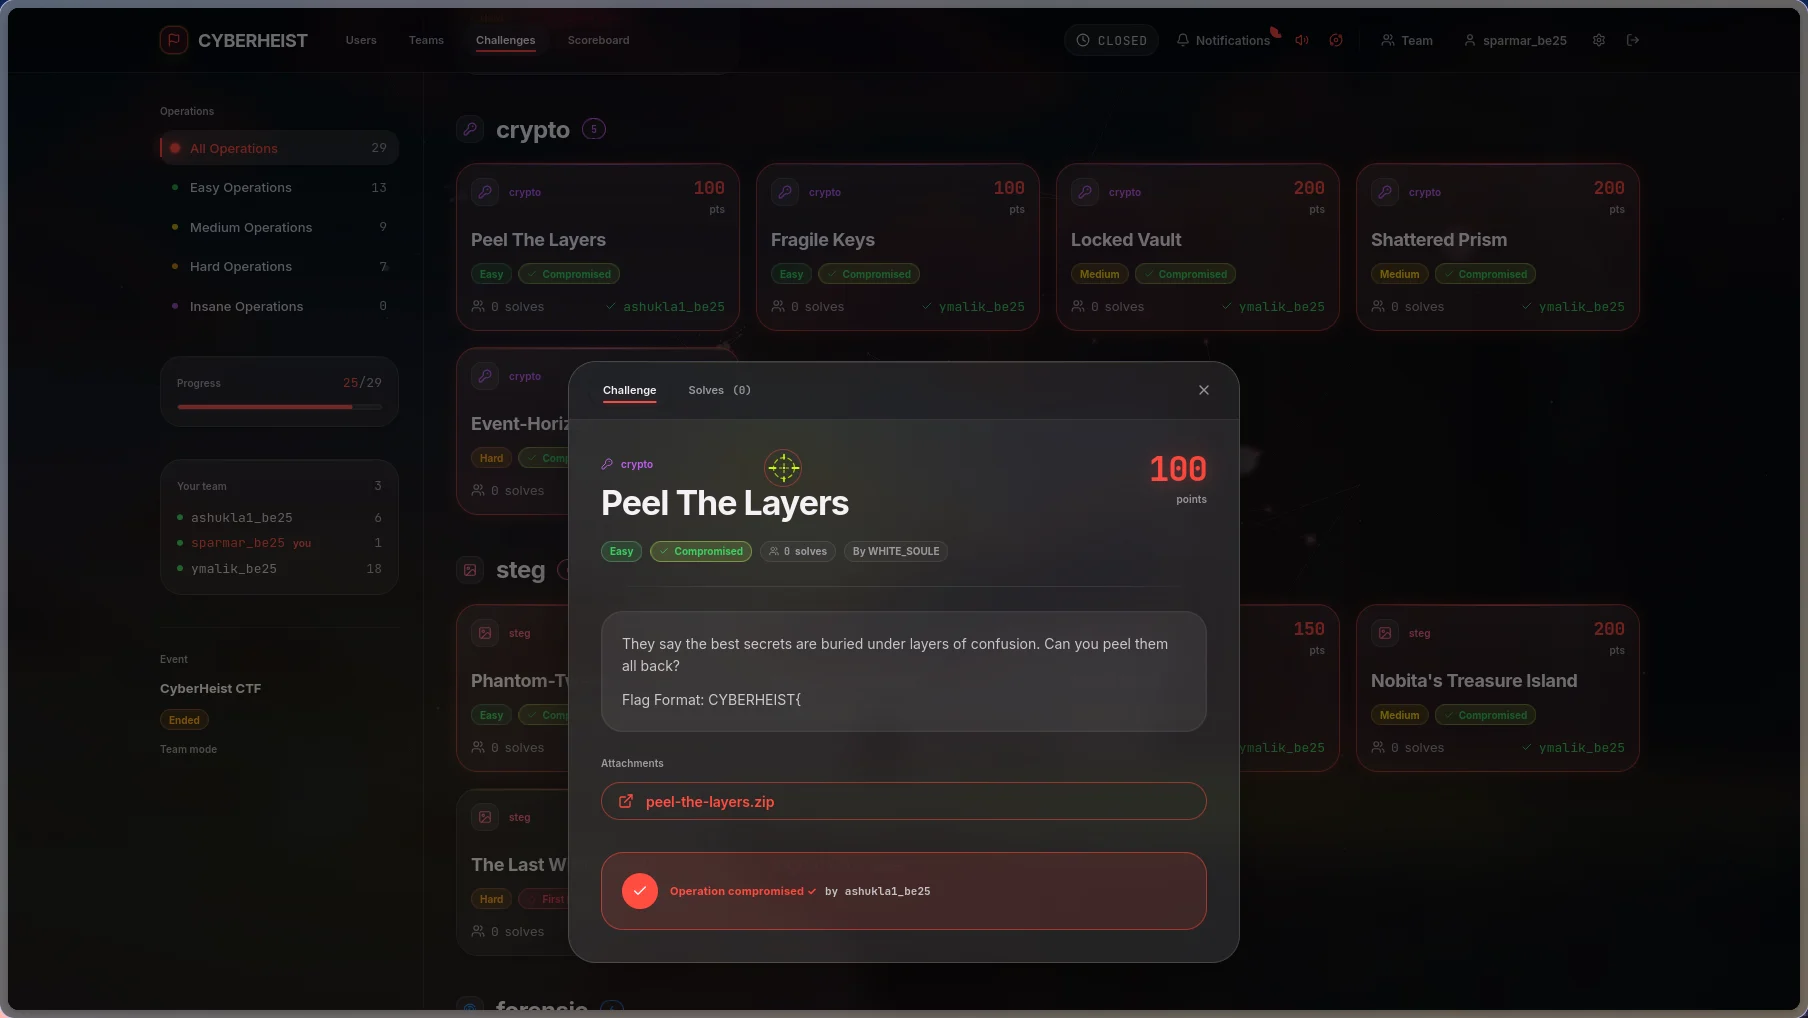
The challenge
Cyber Heist Fragile Keys
First look
Finding the way in
First, we extracted two files from the zipfile, ciphertext.txt and public_key.txt files.
The public key contained the RSA modulus and public exponent (e = 65537), along with the encrypted message.
After examining the RSA parameters, I identified that the two prime factors of the modulus were unusually close to each other.
So, I used Fermat Factorization to recover the two prime numbers.
Then, I calculated Euler's totient function and derived the private exponent (d) using the modular multiplicative inverse.
# the command you ran
The flag
We then used the private key to decrypt the ciphertext and obtained the Flag: CYBERHEIST{f3rm4tf4ct0r1z4t10nbr34k5cl0s3pr1m3s}.
What I learned
One or two things worth remembering for next time.