Ghost Vault
By Srijan Parmar · 1 min read
About the CTF: CyberHeist
Cyber Heist Ghost vault
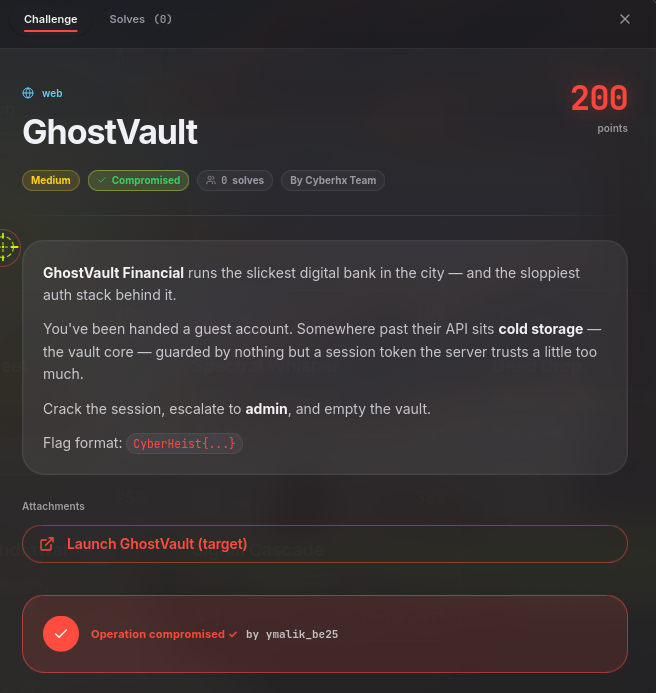
The challenge
Cyber Heist Ghost vault
First look
Finding the way in
First, we inspected the website's JavaScript and found a legacy HS256 authentication method alongside RS256.
We then retrieved the public RSA key and used it to create a forged JWT with admin privileges.
After testing different key formats, we found that adding a trailing newline to the PEM key allowed the forged token to pass authentication.
# the command you ran
The flag
Using the forged token, we gained admin access and opened the restricted vault through account ID 31337.
The server returned the Flag: CyberHeist{4lgc0nfus10nc0ldst0r4g3r41d}.
What I learned
I messed up the flag of clickbait and ghost vault, pls ignore the previous clickbait one