Peel the Layers
By Srijan Parmar · 1 min read
About the CTF: CyberHeist
First, we extracted encoded.txt from the zipfile. We Base64-decoded its contents, which revealed a Base32 string. Decoding that produced hexadecimal text, which we converted into…
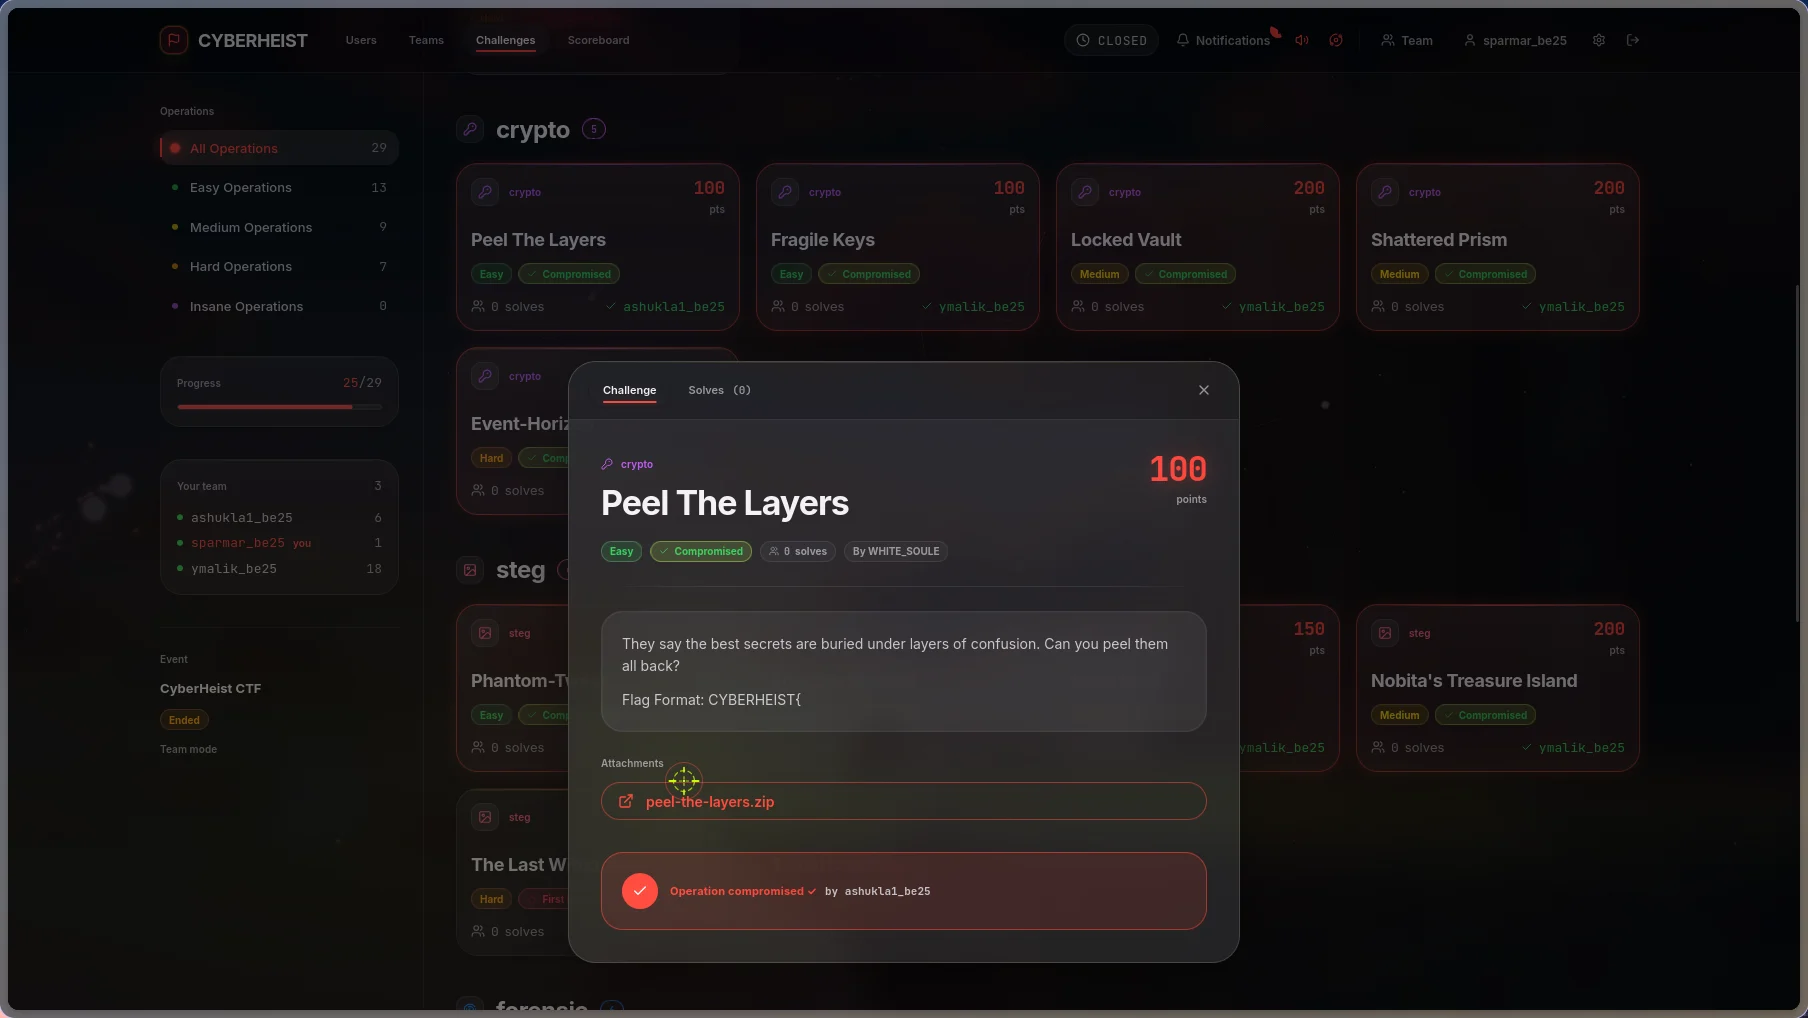
The challenge
Cyber Heist Peel the layers
First look
Finding the way in
First, we extracted encoded.txt from the zipfile.
We Base64-decoded its contents, which revealed a Base32 string.
Decoding that produced hexadecimal text, which we converted into another encoded string.
We reversed this string and Base64-decoded it, revealing text that resembled the flag format but had shifted letters. EZZ
# the command you ran
The flag
Applying ROT13 decryption revealed the Flag: CYBERHEIST{l4y3r50fd3c3pt10n4r3fun}.
What I learned
One or two things worth remembering for next time.